10Identity BrokerIdentity Broker
Identity Sharing과 PDP·PEP가 한 도메인 안에서 PDP→PEP로 신원을 나눠 주는 기본 공유라면, Identity Broker 는 PDP 게이트웨이끼리 신원을 주고받는 더 큰 규모의 공유 방법입니다. 여러 대의 Identity Awareness Security Gateway가 흩어져 있는 분산 환경에서, 서로 다른 관리 도메인(Security Management Server / Domain Management Server)에 걸쳐서도 신원을 전파할 수 있다는 점이 핵심입니다. 이 장은 Identity Broker가 무엇이며 어떻게 동작하는지부터, 구성 파일 $FWDIR/conf/identity_broker.C 의 모든 섹션·파라미터, Publisher·Subscriber를 SmartConsole과 명령줄에서 설정하는 전체 절차, 필터의 모든 종류와 알고리즘, 그리고 4대 게이트웨이로 구성한 완성 예제 까지 원문이 담은 내용을 하나도 빼지 않고 풀어 정리합니다.
Identity Broker란
Identity Broker 는 PDP 게이트웨이(Policy Decision Point) 사이의 신원 공유 방법 입니다. 여러 Identity Awareness Security Gateway가 분산된 환경에서, 한 PDP 게이트웨이가 받은 신원을 다른 PDP 게이트웨이로 전파 할 수 있어, 더 확장성 있고 견고한 계층(hierarchy)과 토폴로지를 만들 수 있습니다.
Identity Broker는 PDP 인스턴스의 Web-API 기반 기능 입니다. 즉 PDP 사이에 새로운 통신 채널을 하나 더 추가하는 셈입니다.
Identity Broker 솔루션이 하는 일
Identity Broker는 PDP 게이트웨이들 사이에서 신원을 전파합니다. 동작 흐름은 이렇습니다 — 한 PDP 게이트웨이가 신원 소스(Identity Source)에서 신원을 배우고, 그룹 멤버십을 조회(group membership query)하고, Access Role을 계산한 뒤, 그 결과를 다른 PDP 게이트웨이들에 공유 합니다. 이렇게 하면 신원을 받는 쪽의 PDP 게이트웨이, 신원 소스, 그리고 User Directory의 부하가 모두 줄 어듭니다.
무엇보다, 이 공유는 서로 다른 Security Management Server / Domain Management Server가 관리하는 PDP 게이트웨이 사이에서도 이루어질 수 있습니다.
Identity Broker 사이의 신원 공유는 필터(filter) 로 제어할 수 있습니다. 구체적으로 다음을 할 수 있습니다.
- 네트워크, 사용자/컴퓨터 이름, 도메인, 신원 소스, Access Role, distinguished name 으로 신원을 필터링 합니다.
- 로컬 신원 세션만 공유 합니다. 이 옵션을 켜면 PDP는 자기가 직접 취득한 세션만 전달 하고, 다른 PDP에서 배운 세션은 전달하지 않 습니다.
Identity Broker 솔루션은 기본적으로 받은 모든 신원을 공유 합니다. 필터를 적용하면, 다른 PDP에게 굳이 필요 없는 신원이 공유되는 것을 막을 수 있습니다.
용어와 설명
| 용어 | 설명 |
|---|---|
| Publisher | 하나 이상의 Subscriber와 신원을 공유 하도록 정의된 Security Gateway. |
| Subscriber | 하나 이상의 Publisher로부터 신원을 받 도록 정의된 Security Gateway. |
Identity Broker 통신 방식
Identity Broker는 WEB-API로 통신 합니다. Security Gateway들은 HTTP POST 요청을 통해 JSON 형식 으로 정보를 주고받습니다.
그리고 각 Identity Broker 노드는 서로를 검증 합니다.
- Publisher 는 Subscriber가 제시한 SSL 인증서(Certificate)를 검증 해서 Subscriber를 확인합니다.
- Subscriber 는 사전 공유 비밀 키(pre-shared secret key)를 검증 해서 Publisher를 확인합니다.
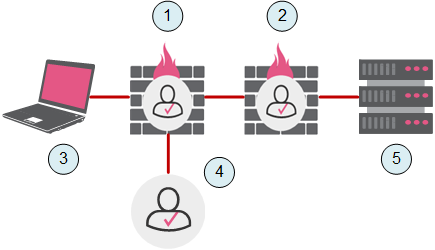
예제 시나리오로 보는 전체 흐름
논리 토폴로지의 각 요소는 다음과 같습니다.
| 항목 | 설명 |
|---|---|
| 1 | Security Gateway #1 |
| 2 | Security Gateway #2 |
| 3 | Security Gateway #1 뒤에 있는 컴퓨터(3) 위의 사용자 |
| 4 | 신원 소스(Identity Source) — 예: Active Directory |
| 5 | Security Gateway #2 뒤에 있는 리소스(resource) — 예: 서버 |
이 구성에서 일어나는 일의 일반적인 사건 흐름(General Flow of Events) 은 다음과 같습니다.
- Security Gateway #1 을 Identity Broker Publisher 로 구성합니다. 이 게이트웨이는 신원 소스(4)에서 신원을 얻어 배우고, 그것을 원격의 Security Gateway #2에 공유합니다.
- Security Gateway #2 를 Identity Broker Subscriber 로 구성합니다. 이 게이트웨이는 원격의 Security Gateway #1로부터 사용자들의 신원을 받습니다.
- 사용자가 리소스(5)에 접속하면, Security Gateway #2가 그 사용자를 식별하고 신원 기반 규칙을 적용 합니다.
- (선택) 필터를 적용 해 Security Gateway #1이 어떤 신원을 게시하는지, Security Gateway #2가 어떤 신원을 구독하는지 제어할 수 있습니다.
- (선택) Security Gateway #1과 Security Gateway #2를 서로 다른 Management Server로 관리 할 수 있습니다.
구성 파일 `identity_broker.C`
Identity Broker는 Security Gateway(클러스터라면 각 Cluster Member) 에 있는 $FWDIR/conf/identity_broker.C 파일에서 구성합니다. 이 파일을 다루기 전에 알아 둘 점이 몇 가지 있습니다.
`identity_broker.C` 파일 템플릿
$FWDIR/conf/identity_broker.C 파일의 예시 템플릿은 세 가지 역할에 맞춰 준비되어 있습니다.
- PDP Publisher 로 동작하는 Security Gateway
- PDP Subscriber 로 동작하는 Security Gateway
- PDP Publisher 이자 PDP Subscriber 로 동작하는 Security Gateway
PDP Publisher용 — 필수 파라미터 템플릿
다음은 두 개의 PDP Subscriber와 동작하는 PDP Publisher 에 Identity Broker를 구성하는 데 필요한 필수 파라미터만 담은 템플릿입니다.
#  Configuration file for Identity Broker - Identity Distribution between PDPs.
#  For more information, please refer to Identity Awareness Admin Guide.
#############################################################
(
  :sharing_id (ENTER_UNIQUE_SHARING_ID_FOR_THIS_PUBLISHER_GATEWAY)
  :identity_subscribers (
    : (
      :Name (DESCRIPTIVE_NAME_OF_SUBSCRIBER_GATEWAY_1)
      :sharing_id (UNIQUE_SHARING_ID_OF_SUBSCRIBER_GATEWAY_1)
      :ipaddr (IP_ADDRESS_OF_INTERFACE_ON_SUBSCRIBER_GATEWAY_1)
      :certificate_subject ("CERTIFICATE_SUBJECT_OF_SUBSCRIBER_GATEWAY_1")
    )
    : (
      :Name (DESCRIPTIVE_NAME_OF_SUBSCRIBER_GATEWAY_2)
      :sharing_id (UNIQUE_SHARING_ID_OF_SUBSCRIBER_GATEWAY_2)
      :ipaddr (IP_ADDRESS_OF_INTERFACE_ON_SUBSCRIBER_GATEWAY_2)
      :certificate_subject ("CERTIFICATE_SUBJECT_OF_SUBSCRIBER_GATEWAY_2")
    )
  )
)
PDP Subscriber용 — 필수 파라미터 템플릿
다음은 두 개의 PDP Publisher와 동작하는 PDP Subscriber 에 Identity Broker를 구성하는 데 필요한 필수 파라미터만 담은 템플릿입니다.
#  Configuration file for Identity Broker - Identity Distribution between PDPs.
#  For more information, please refer to Identity Awareness Admin Guide.
#############################################################
(
  :sharing_id (ENTER_UNIQUE_SHARING_ID_FOR_THIS_SUBSCRIBER_GATEWAY)
  :identity_publishers (
    : (
      :Name (DESCRIPTIVE_NAME_OF_PUBLISHER_GATEWAY_1)
      :sharing_id (UNIQUE_SHARING_ID_OF_PUBLISHER_GATEWAY_1)
      :ipaddr (IP_ADDRESS_OF_INTERFACE_ON_PUBLISHER_GATEWAY_1)
    )
    : (
      :Name (DESCRIPTIVE_NAME_OF_PUBLISHER_GATEWAY_2)
      :sharing_id (UNIQUE_SHARING_ID_OF_PUBLISHER_GATEWAY_2)
      :ipaddr (IP_ADDRESS_OF_INTERFACE_ON_PUBLISHER_GATEWAY_2)
    )
  )
)
Publisher 겸 Subscriber용 — 지원되는 모든 파라미터 템플릿
다음 템플릿은 Identity Broker를 구성하는 데 쓸 수 있는 모든 지원 파라미터 를 담고 있습니다. 앞서 강조했듯, 모든 파라미터는 괄호 안에 값이 있어야 하고, 값이 없는 선택적 파라미터는 파일에서 삭제 해야 합니다.
#  Configuration file for Identity Broker - Identity Distribution between PDPs.
#  For more information, see the Identity Awareness Administration Guide.
####################################################################
(
  :sharing_id ()
  :identity_subscribers (
    : (
      :Name ()
      :sharing_id ()
      :ipaddr ()
      :certificate_subject ("")
      :crl_validation_config (fail_closed)
      :share_only_local_sessions (false)
      :filter (
        :include_users_and_machines ()
        :exclude_users_and_machines ()
        :include_networks ()
        :exclude_networks ()
        :include_identity_source ()
        :exclude_identity_source ()
        :include_domains ()
        :exclude_domains ()
        :include_roles ()
        :exclude_roles ()
        :include_distinguished_names ()
        :exclude_distinguished_names ()
        :include_owners ()
        :exclude_owners ()
        :include_immediate_publishers ()
        :exclude_immediate_publishers ()
      )
    )
  )
  :identity_publishers (
    : (
      :Name ()
      :sharing_id ()
      :ipaddr ()
      :recalculate_access_roles (false)
      :filter (
        :include_users_and_machines ()
        :exclude_users_and_machines ()
        :include_networks ()
        :exclude_networks ()
        :include_identity_source ()
        :exclude_identity_source ()
        :include_domains ()
        :exclude_domains ()
        :include_roles ()
        :exclude_roles ()
        :include_distinguished_names ()
        :exclude_distinguished_names ()
        :include_owners ()
        :exclude_owners ()
        :include_immediate_publishers ()
        :exclude_immediate_publishers ()
      )
    )
  )
  :global_outgoing_filter (
    :include_users_and_machines ()
    :exclude_users_and_machines ()
    :include_networks ()
    :exclude_networks ()
    :include_identity_source ()
    :exclude_identity_source ()
    :include_domains ()
    :exclude_domains ()
    :include_roles ()
    :exclude_roles ()
    :include_distinguished_names ()
    :exclude_distinguished_names ()
    :include_owners ()
    :exclude_owners ()
    :include_immediate_publishers ()
    :exclude_immediate_publishers ()
  )
  :global_incoming_filter (
    :include_users_and_machines ()
    :exclude_users_and_machines ()
    :include_networks ()
    :exclude_networks ()
    :include_identity_source ()
    :exclude_identity_source ()
    :include_domains ()
    :exclude_domains ()
    :include_roles ()
    :exclude_roles ()
    :include_distinguished_names ()
    :exclude_distinguished_names ()
    :include_owners ()
    :exclude_owners ()
    :include_immediate_publishers ()
    :exclude_immediate_publishers ()
  )
)
파일의 섹션 구조
$FWDIR/conf/identity_broker.C 파일은 크게 다섯 개의 섹션으로 나뉩니다. 어떤 섹션이 필수(Mandatory)이고 어떤 것이 선택(Optional)인지는 게이트웨이가 Publisher인지 Subscriber인지에 따라 달라집니다.
| # | 섹션 | 유형 | 설명 |
|---|---|---|---|
| 1 | Sharing ID (:sharing_id ()) | Publisher·Subscriber 모두 필수 | 이 Security Gateway가 다른 Security Gateway와 통신할 때 자신을 식별 하는 값. 영숫자(alphanumeric)로 된 고유 식별자 입니다. |
| 2 | Identity Subscribers (:identity_subscribers ()) | Publisher에서 필수 | PDP Publisher로 동작하는 게이트웨이에서 Identity Subscriber들을 구성 합니다. |
| 3 | Identity Publishers (:identity_publishers ()) | Subscriber에서 필수 | PDP Subscriber로 동작하는 게이트웨이에서 Identity Publisher들을 구성 합니다. |
| 4 | Global Outgoing Filters (:global_outgoing_filter ()) | Publisher에서 선택 | 이 Publisher가 자신에게 구성된 모든 Subscriber에게 보내는 모든 신원 세션 에 적용되는 전역 송신 필터. |
| 5 | Global Incoming Filters (:global_incoming_filter ()) | Subscriber에서 선택 | 이 Subscriber가 자신에게 구성된 모든 Publisher로부터 받는 모든 신원 세션 에 적용되는 전역 수신 필터. |
Identity Subscribers 섹션 에서 필수 파라미터는 :Name (), :sharing_id (), :ipaddr (), :certificate_subject ("") 이고, 선택 파라미터는 :crl_validation_config (), :share_only_local_sessions (), 그리고 여러 개의 로컬 필터를 담을 수 있는 :filter () 입니다.
Identity Publishers 섹션 에서 필수 파라미터는 :Name (), :sharing_id (), :ipaddr () 이고, 선택 파라미터는 :recalculate_access_roles () 과 :filter () 입니다.
Identity Broker 구성하기
PDP Publisher 구성하기
Publisher Security Gateway는 Identity Subscriber로 여겨지는 다른 Security Gateway들과 신원을 공유 합니다. Publisher가 신원을 공유하려면, Publisher의 $FWDIR/conf/identity_broker.C 파일에 Identity Subscriber들을 구성 해야 합니다.
1/2 단계 — SmartConsole에서의 PDP Publisher 구성
- 왼쪽 탐색 패널에서 Gateways & Servers 를 클릭합니다.
- Security Gateway / Cluster 객체를 더블 클릭합니다.
- Identity Awareness Software Blade를 활성화하고, Identity Awareness 구성 마법사(Configuration wizard)를 완료합니다.
- 왼쪽 트리에서 Identity Awareness 를 클릭합니다.
- 해당하는 신원 소스(Identity Sources) — 신원을 가져올 Identity Provider들 — 를 선택합니다. 선택한 각 신원 소스 옆의 Settings 를 클릭해 해당 설정을 구성합니다.
- (선택) 이 Security Gateway / Cluster를 다른 Identity Awareness Security Gateway / Cluster의 Subscriber 로도 구성합니다.
- OK 를 클릭합니다.
- 이 Security Gateway / Cluster 객체에 Access Control Policy를 설치 합니다.
2/2 단계 — 명령줄에서의 PDP Publisher 구성
- 이 Security Gateway(클러스터라면 각 Cluster Member)의 명령줄에 접속합니다.
- Expert mode 로 로그인합니다.
- 현재 파일을 백업합니다.
cp -v $FWDIR/conf/identity_broker.C{,_BKP}
- 현재 파일을 편집합니다.
vi $FWDIR/conf/identity_broker.C
:sharing_id ()섹션에 이 PDP Publisher의 영숫자 고유 식별자 를 입력합니다. 최소 16자 이상 으로 넣으며, UUID 생성기를 사용해도 됩니다. 이 식별자는 Subscriber들의$FWDIR/conf/identity_broker.C파일에서:identity_publishers ()섹션에 쓰게 됩니다.
:sharing_id (b2L4Sri5K9HxJw63GjAb)
:identity_subscribers ()섹션에, 각 Subscriber Security Gateway / Cluster에 해당하는 데이터를 입력합니다.
각 Subscriber에 입력하는 파라미터는 다음과 같습니다.
| 파라미터 | 설명 |
|---|---|
Name | 이 Subscriber Security Gateway / Cluster를 가리키는 설명용 이름 . |
sharing_id | Subscriber의 고유 식별자. Subscriber의 $FWDIR/conf/identity_broker.C 파일 맨 위 :sharing_id () 섹션 에서 이 값을 가져옵니다. |
ipaddr | 이 Publisher가 연결할, Subscriber 쪽 해당 인터페이스의 IPv4 주소 . |
certificate_subject | Subscriber의 인증서 Subject(아래 절차로 취득). |
certificate_subject 설정 절차 는 다음과 같습니다.
a. Subscriber로부터 서버 인증서(Server Certificate) 를 가져옵니다. Publisher Security Gateway(각 Cluster Member)에서 다음을 실행합니다.
$FWDIR/bin/BrokerCertFetcher <IP Address of Subscriber>
b. CA Fingerprint와 Subscriber Security Gateway의 "Subject"가 올바른지 확인합니다.
c. Subscriber Security Gateway의 "Subject"를 certificate_subject 필드에 구성합니다.
d. 다음 파일이 존재하는지 확인합니다.
stat $FWDIR/nac/broker_ca_certs/<IP_Address_of_Subscriber>.pem
Subscriber 항목에 줄 수 있는 선택 파라미터 는 다음과 같습니다.
| 파라미터 | 설명 |
|---|---|
crl_validation_config | (선택) CRL(Certificate Revocation List, 인증서 폐기 목록) 검증 모드. 아래 세 가지 중 하나. |
share_only_local_sessions | (선택) 이 Subscriber에게 로컬 세션만 게시 할지. true / false(기본). 로컬 세션이란 로컬에 연결된 신원 소스에서 직접 배운 신원입니다. |
filter | (선택) 이 특정 Subscriber에 대한 송신(outgoing) 필터 . 아래 "Identity 필터 구성하기" 참고. |
crl_validation_config 의 옵션은 다음과 같습니다.
| 값 | 의미 |
|---|---|
fail_closed | CRL 목록 다운로드를 시작하고, 다운로드가 실패하면 연결을 거부 합니다(기본값). |
fail_open | CRL 목록 다운로드를 시작하고, 다운로드가 실패해도 연결을 허용 합니다. |
skip_crl_check | CRL을 인증서 검증에 사용하지 않 습니다. |
PDP Subscriber 구성하기
Subscriber Security Gateway는 Identity Publisher로 여겨지는 다른 Security Gateway들로부터 신원을 받 습니다. Subscriber가 신원을 받으려면, Subscriber의 $FWDIR/conf/identity_broker.C 파일에 Identity Publisher들을 구성 해야 합니다.
1/2 단계 — SmartConsole에서의 PDP Subscriber 구성
- 왼쪽 탐색 패널에서 Gateways & Servers 를 클릭합니다.
- Security Gateway / Cluster 객체를 더블 클릭합니다.
- Identity Awareness Software Blade를 활성화하고 Identity Awareness 구성 마법사를 완료합니다.
- 왼쪽 트리에서 Identity Awareness > Identity Sharing 을 클릭합니다.
- 오른쪽 창에서: a. Get Identities from Identity Broker 를 활성화합니다. b. Settings 를 클릭합니다 — Portal Access Settings 창이 열립니다.
- Subscriber가 Publisher들에게 HTTPS 서버 인증서로 제시할, 전용 내부 CA 인증서를 가져옵니다(Import) . a. Management Server의 명령줄에 접속합니다. b. Expert mode로 로그인합니다. c. 구성하려는 Security Gateway / Cluster 객체에 대해 다음 명령을 실행합니다.
cpca_client create_cert -n "CN=<Name of Security Gateway / Cluster Object>.broker.portal" -f <Name of Security Gateway / Cluster Object>_broker.p12 -k IKE -w "<Password>"
d. 이 P12 파일을 Management Server에서 SmartConsole 클라이언트 컴퓨터로 옮깁니다. e. Certificate 섹션에서 Import 를 클릭합니다. f. P12 파일을 선택하고 Open 을 클릭합니다. 7. Accessibility 설정을 구성합니다. 기본적으로 Publisher Security Gateway는 Subscriber Security Gateway의 내부 인터페이스로 접속을 시도 합니다. 만약 어떤 Publisher가 다른 인터페이스를 통해 Subscriber에 접속한다면: a. Accessibility 섹션에서 Edit 를 클릭합니다. b. 해당하는 옵션을 선택합니다. c. OK 를 클릭해 Portal Access Settings 창을 닫습니다. 8. OK 를 클릭합니다. 9. Security Gateway / Cluster 객체에 Access Control Policy를 설치 합니다.
2/2 단계 — 명령줄에서의 PDP Subscriber 구성
- Subscriber Security Gateway(클러스터라면 각 Cluster Member)의 명령줄에 접속합니다.
- Expert mode 로 로그인합니다.
- 현재 파일을 백업합니다.
cp -v $FWDIR/conf/identity_broker.C{,_BKP}
- 현재 파일을 편집합니다.
vi $FWDIR/conf/identity_broker.C
:sharing_id ()섹션에 이 PDP Subscriber의 영숫자 고유 식별자 를 입력합니다. 최소 16자 이상 , UUID 생성기 사용 가능. 이 식별자는 Publisher들의 파일에서:identity_subscribers ()섹션에 쓰게 됩니다.
:sharing_id (b2L4Sri5K9HxJw63GjAb)
:identity_publishers ()섹션에 각 Publisher Security Gateway / Cluster에 해당하는 데이터를 입력합니다.
| 파라미터 | 설명 |
|---|---|
Name | 이 Publisher Security Gateway / Cluster를 가리키는 설명용 이름 . |
sharing_id | Publisher의 고유 식별자. Publisher의 $FWDIR/conf/identity_broker.C 파일 맨 위 :sharing_id () 섹션 에서 가져옵니다. |
ipaddr | 이 Subscriber가 연결할, Publisher 쪽 해당 인터페이스의 IPv4 주소 . |
filter | (선택) 이 특정 Publisher에 대한 수신(incoming) 필터 . |
recalculate_access_roles | (선택) 이 Publisher에서 공유된 각 세션에 대해 Access Role을 다시 계산 할지. |
recalculate_access_roles 를 켜면(true), Subscriber가 Publisher가 보낸 Access Role 대신, 자신의 Access Control Policy에 있는 Access Role을 사용 할 수 있습니다. 이 기능은 기본적으로 비활성화 되어 있습니다. 자세한 내용은 sk164474를 참고하세요.
Identity Broker 필터
기본 동작은 다음과 같습니다.
- Publisher는 모든 신원 세션을 자신의 모든 Subscriber에게 보냅 니다.
- Subscriber는 모든 신원 세션을 자신의 모든 Publisher로부터 받 습니다.
$FWDIR/conf/identity_broker.C 파일에 필터를 구성 하면 Identity Broker 사이의 신원 공유를 제어할 수 있습니다.
Publisher 에서는 다음을 구성할 수 있습니다.
- Global(전역) 필터 — 이 Publisher가 자신에게 구성된 모든 Subscriber에게 보내는 모든 신원 세션 에 적용됩니다. 전역 필터는 로컬 필터보다 우선 합니다.
- Local(로컬) 필터 — 이 Publisher가 특정 Subscriber에게 보내는 신원 세션에 적용됩니다.
Subscriber 에서는 다음을 구성할 수 있습니다.
- Global 필터 — 이 Subscriber가 모든 Publisher로부터 받는 모든 신원 세션 에 적용됩니다. 전역 필터가 로컬 필터보다 우선 합니다.
- Local 필터 — 이 Subscriber가 특정 Publisher로부터 받는 신원 세션에 적용됩니다.
필터 알고리즘 — include와 exclude
필터에는 include 필터 와 exclude 필터 두 종류 가 있습니다. Security Gateway에서의 적용 알고리즘은 이렇습니다.
- 구성되어 있다면 include 필터를 적용 합니다. "AND"(그리고)
- 구성되어 있다면 exclude 필터를 적용 합니다.
exclude 필터에 여러 구문(statement)이 들어 있으면, Security Gateway는 그 exclude 구문들 사이에 논리 "OR"(또는) 연산을 수행합니다.
필터 종류별 사용법
사용자/컴퓨터 이름(Users/Machines name) — 예를 들어 사용자 johndoe 또는 srv_ 로 시작하는 모든 사용자를 제외하려면:
:exclude_users_and_machines (
: ("johndoe")
: ("regexp:^srv_*$")
)
네트워크(Network) — 예를 들어 192.168.0.1/24 네트워크의 세션만 포함하려면:
:include_networks (192.168.0.1/255.255.255.0)신원 소스(Identity Source) — 사용 가능한 신원 소스 중 어느 것에서 온 모든 신원을 제외하거나 포함합니다. 이 필터에 쓸 수 있는 신원 소스는 다음과 같습니다 — Portal, Identity Agent, Remote Access, AD Query, Terminal Servers Identity Agent, RADIUS Accounting, Identity Awareness API, Identity Collector. 예를 들어 Identity Collector에서 온 모든 신원을 제외하려면:
:exclude_identity_source (
: ("Identity Collector")
)
도메인 이름(Domain Name) — 정규식 사용 가능. 예를 들어 도메인 example.com 의 모든 신원, 또는 company.com 으로 끝나는 도메인의 모든 신원을 제외하려면:
:exclude_domains (
: ("example.com")
: ("regexp:^.*company\.com$")
)
Distinguished Name — 정규식 사용 가능. 예를 들어 조직 단위(OU) "OU_01" 을 포함하는 distinguished name을 가진 모든 신원을 포함하려면:
:include_distinguished_names (
: ("regexp:^.*OU=OU_01.*$")
)
Access Role — 특정 Access Role에 매칭된 신원을 제외하거나 포함하려면, 해당 Access Role 객체 이름을 지정합니다. 정규식 사용 가능. 예를 들어 "UK_Finance" Access Role과 "Manager_" 로 시작하는 Access Role에 매칭되는 신원만 보내려면:
:include_roles (
: ("UK_Finance")
: ("regexp:^Manager_.*$")
)
Immediate Publishers(직접 Publisher) — Immediate Publisher란 신원을 한 홉(hop) 떨어진 Identity Broker로 전파하는 게이트웨이 입니다. 즉 두 Identity Broker 피어 사이에 직접적인 publisher-subscribe 연결 이 존재한다는 뜻입니다. 구성된 Subscriber들의 Immediate Publisher를 제외/포함하려면 필터 집합에 하나 이상 지정합니다.
:include_immediate_publishers (
: ("192.168.1.72")
: ("192.168.1.66")
)Immediate Owners(직접 소유자) — PDP 인스턴스는 신원 소스에서 배운 로그인 이벤트를 바탕으로 신원 세션을 생성 합니다. 예를 들어 어떤 Identity Agent가 특정 PDP 인스턴스에서 종료(terminate)되면, 그 PDP 인스턴스가 신원 세션을 만들고 그 세션의 소유자(owner)가 됩 니다. 이 PDP 인스턴스가 그 신원 세션을 구독하는 Identity Broker 피어에 게시할 때, 자신의 IP 주소를 신원 세션 속성의 "owner"로 포함 시킵니다.
다음은 IP 주소 192.168.51.229를 가진 Identity Broker가 신원 세션 94a9f4c를 소유하는 예입니다.
Session:                94a9f4c2
Session UUID:           {B4E4634F-E98E-FCE7-A52B-CCB38B5705DB}
Ip:                     192.168.51.188
Users:                  alice {94fbed73}
Groups:                 InternalSales;All Users
Roles:                  InternalSalesAccessRole
Client Type:            portal
Authentication Method:  User & Password
Distinguished Name:
Connect Time:           Thu Jan 9 16:00:27 2020
Next Reauthentication:  -
Next Connectivity Check: -
Next Ldap Fetch:        -
Packet Tagging Status:  Not Active
Published Gateways:     Local
Owner:                  192.168.51.229
Immediate Publisher:    192.168.51.229
Published PDPs:         192.168.51.226
특정 소유자로부터 온 신원을 제외하거나 포함하려면, 해당 소유자의 IP 주소를 지정합니다.
예를 들어 두 특정 소유자에서 비롯된 신원만 공유하려면:
:include_owners (
: ("172.23.106.72")
: ("172.23.106.66")
)
전역 필터 (선택)
global_outgoing_filter 와 global_incoming_filter 파라미터로 Identity Broker에 전역 필터를 구성할 수 있습니다.
| 파라미터 | 설명 |
|---|---|
global_outgoing_filter | Publisher의 전역 송신 필터 . 구성된 모든 Subscriber에게 게시되는 모든 신원 세션 에 적용됩니다. |
global_incoming_filter | Subscriber의 전역 수신 필터 . 구성된 모든 Publisher로부터 받는 모든 신원 세션 에 적용됩니다. |
Identity 필터 구성하기 — 전체 템플릿
다음은 가능한 모든 필터 구성 템플릿입니다.
로컬 필터 :filter 와 전역 필터 :global_outgoing_filter, :global_incoming_filter 는 모두 같은 내부 항목 집합 을 가집니다.
:filter (
  :include_users_and_machines ()
  :exclude_users_and_machines ()
  :include_networks ()
  :exclude_networks ()
  :include_identity_source ()
  :exclude_identity_source ()
  :include_domains ()
  :exclude_domains ()
  :include_roles ()
  :exclude_roles ()
  :include_distinguished_names ()
  :exclude_distinguished_names ()
  :include_owners ()
  :exclude_owners ()
  :include_immediate_publishers ()
  :exclude_immediate_publishers ()
)
:global_outgoing_filter (
:include_users_and_machines ()
:exclude_users_and_machines ()
:include_networks ()
:exclude_networks ()
:include_identity_source ()
:exclude_identity_source ()
:include_domains ()
:exclude_domains ()
:include_roles ()
:exclude_roles ()
:include_distinguished_names ()
:exclude_distinguished_names ()
:include_owners ()
:exclude_owners ()
:include_immediate_publishers ()
:exclude_immediate_publishers ()
):global_incoming_filter (
:include_users_and_machines ()
:exclude_users_and_machines ()
:include_networks ()
:exclude_networks ()
:include_identity_source ()
:exclude_identity_source ()
:include_domains ()
:exclude_domains ()
:include_roles ()
:exclude_roles ()
:include_distinguished_names ()
:exclude_distinguished_names ()
:include_owners ()
:exclude_owners ()
:include_immediate_publishers ()
:exclude_immediate_publishers ()
)구성 완료 예제 — 4대 게이트웨이
다음은 네 대의 Security Gateway로 Identity Broker를 구성한 완성 예제입니다. 논리 토폴로지에서 각 게이트웨이가 어떤 Publisher로부터 신원을 받고, 어떤 Subscriber와 신원을 공유 하는지를 표로 정리하면 다음과 같습니다.
| Security Gateway | 신원을 받는 PDP Publisher | 신원을 공유하는 PDP Subscriber |
|---|---|---|
| Security Gateway #1 | 없음 | Security Gateway #3 (10.10.10.x 경유) |
| Security Gateway #2 | 없음 | Security Gateway #3 (10.10.10.x 경유) |
| Security Gateway #3 | Security Gateway #1 (10.10.10.x), Security Gateway #2 (10.10.10.x) | Security Gateway #4 (192.168.10.x 경유) |
| Security Gateway #4 | Security Gateway #3 (192.168.10.x) | 없음 |
즉 #1과 #2는 순수 Publisher, #4는 순수 Subscriber이고, #3은 #1·#2의 Subscriber이면서 동시에 #4의 Publisher 인 중간 계층 역할을 합니다.
Security Gateway #1 의 $FWDIR/conf/identity_broker.C 파일:
  :sharing_id (z8JXd28t0taHnhifKnYm8)
  :identity_subscribers (
    : (
      :Name (GW3)
      :sharing_id (Ac65e4dCc4aBa06b140dE)
      :ipaddr (10.10.10.3)
      :certificate_subject ("GW3.broker.portal")
      :share_only_local_sessions (false)
      :filter ()
    )
  )
  :global_outgoing_filter (
    :exclude_identity_source (
      : ("Identity Collector")
    )
  )
)
Security Gateway #2 의 $FWDIR/conf/identity_broker.C 파일:
  :sharing_id (Y2l885i5u49xJw63hHACP)
  :identity_subscribers (
    : (
      :Name (GW3)
      :sharing_id (Ac65e4dCc4aBa06b140dE)
      :ipaddr (10.10.10.3)
      :certificate_subject ("GW3.broker.portal")
      :share_only_local_sessions (false)
      :filter ()
    )
  )
  :global_outgoing_filter (
    :exclude_identity_source (
      : ("Identity Collector")
    )
  )
)
Security Gateway #3 의 $FWDIR/conf/identity_broker.C 파일 — #3은 #4를 Subscriber로 두고, #1·#2를 Publisher로 둡니다.
  :sharing_id (Ac65e4dCc4aBa06b140dE)
  :identity_subscribers (
    : (
      :Name (GW4)
      :sharing_id (0N8NbkP0XMuvAw3F62d20)
      :ipaddr (192.168.10.4)
      :certificate_subject ("GW4.broker.portal")
      :share_only_local_sessions (false)
      :filter ()
    )
  )
  :identity_publishers (
    : (
      :Name (GW1)
      :sharing_id (z8JXd28t0taHnhifKnYm8)
      :ipaddr (10.10.10.1)
      :filter ()
    )
    : (
      :Name (GW2)
      :sharing_id (Y2l885i5u49xJw63hHACP)
      :ipaddr (10.10.10.2)
      :filter ()
    )
  )
  :global_outgoing_filter (
    :exclude_identity_source (
      : ("Identity Collector")
    )
  )
  :global_incoming_filter (
    :exclude_networks (
      : (192.168.1.0/255.255.255.0)
    )
    :exclude_identity_source (
      : ("Radius Accounting")
    )
  )
)
Security Gateway #4 의 $FWDIR/conf/identity_broker.C 파일 — #4는 #3을 Publisher로 둡니다.
  :sharing_id (0N8NbkP0XMuvAw3F62d20)
  :identity_publishers (
    : (
      :Name (GW3)
      :sharing_id (Ac65e4dCc4aBa06b140dE)
      :ipaddr (10.10.10.3)
      :filter ()
    )
  )
  :global_incoming_filter (
    :exclude_networks (
      : (172.33.40.0/255.255.255.0)
    )
    :exclude_identity_source (
      : ("Radius Accounting")
    )
  )
)
이렇게 같은 sharing_id 값이 한쪽에서는 :sharing_id 로, 다른 쪽에서는 :identity_subscribers 또는 :identity_publishers 안에서 서로를 가리키며 짝을 이룹니다. 예를 들어 #3의 최상위 sharing_id (Ac65e4dCc4aBa06b140dE) 는 #1·#2의 identity_subscribers 와 #4의 identity_publishers 양쪽에서 동일하게 참조됩니다. Identity Broker의 모니터링과 제어에는 Identity Sharing과 PDP·PEP 장에서 다루는 pdp broker 계열 명령을 사용합니다.